Foreign Threats Don't Always Need Malware. They Need Trust.
Earlier this month, the CEO of a major tech company admitted to having a romantic relationship with a woman who U.S. officials believe was in the pay of a foreign government. The investigation is ongoing, but as of today, the company does not believe she was able to obtain sensitive information.
How Anyone Can Become a Target for Foreign Operatives
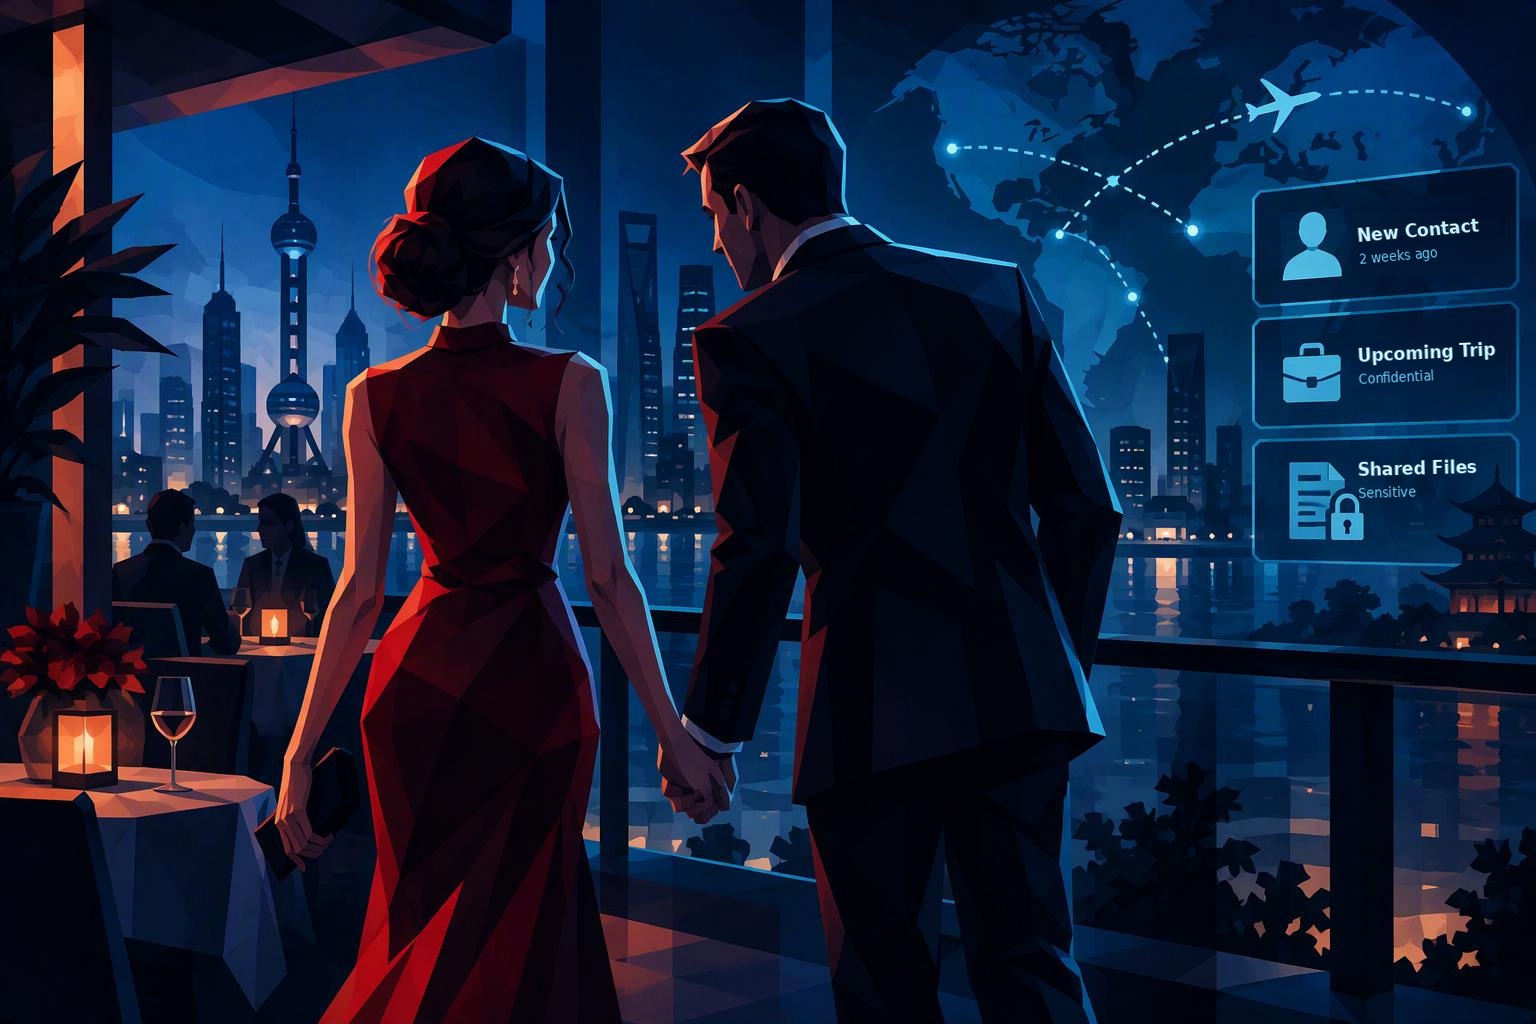
The tactic will be familiar to anyone who is a fan of spy movies: A foreign agent approaches a target with a networking opportunity, a consulting gig, or an invitation for a date. The agent cultivates a legitimate relationship to build trust, then uses that trust to gain access and influence.
You might think that intelligence agents only target industry and government leaders, but that’s far from the truth.
• Fortune 500 executives and government officials are not the only targets. In fact, engineers, developers, data scientists, sales leaders, and admins with privileged access are often easier to reach and less protected.
• Companies without government contracts still have intellectual property valuable to foreign countries, whether it’s chip designs, customer lists, or sales data.
Why Traditional Security Controls May Fail To Detect Foreign Threats
Intelligence agents commonly operate through trusted relationships and legitimate users. This often makes suspicious activity difficult to distinguish from normal operations, especially because foreign threat actors usually use valid credentials and approved applications.
Security controls may validate access and monitor defined channels, but they do not assess intent. In other words, logs may track who, what, where, and when, but they miss the why. As a result, organizations often can’t identify compromises until after sensitive information has been viewed, shared, or exfiltrated. This forces security teams to switch to expensive recovery modes, reacting to breaches instead of preventing them.
InnerActiv is different. By monitoring activity on the endpoint, it can catch the moment trust turns into risk. Here’s how:
How InnerActiv Counters Five Common Intelligence Collection Tactics
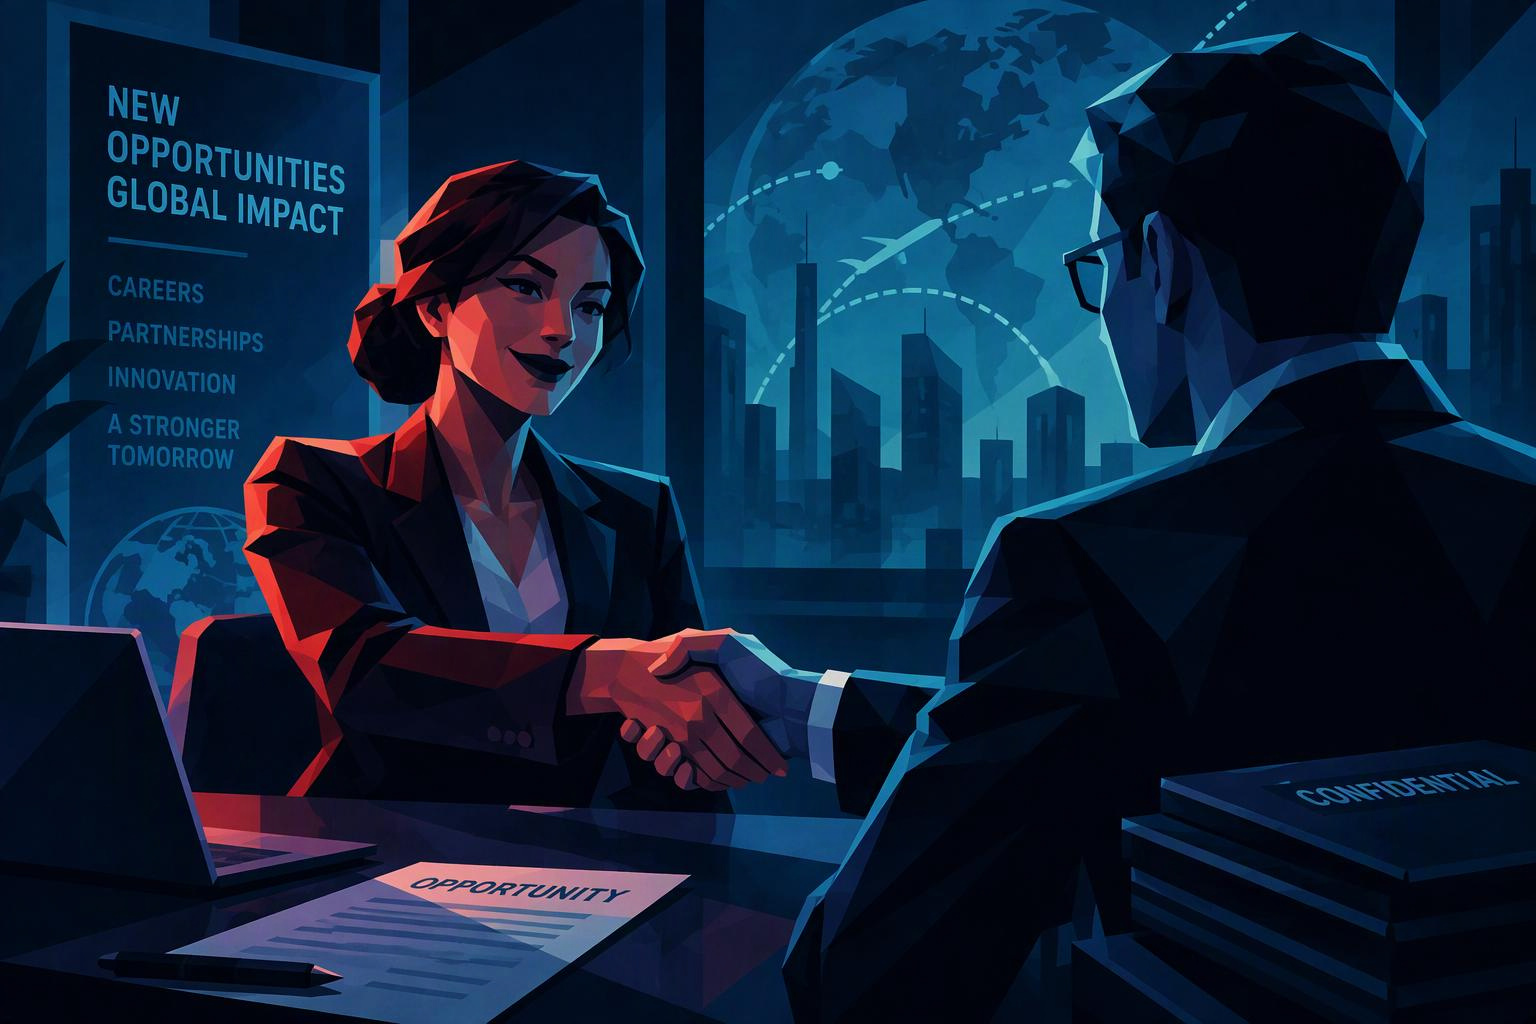
1. Relationship-based access: An agent cultivates a personal or romantic relationship, often over months. The goal is proximity: conversations, introductions, travel schedules, and influence.
InnerActiv detects unusual behavior after a new contact appears, including off-hours access, bulk exports, and files moving to personal channels.
2. Business partners as cover: By posing as customers, resellers, suppliers, or investors, foreign agents can develop trusted relationships with executives and engineers, and access proprietary systems.
InnerActiv sees when employees share sensitive pricing, roadmaps, or controlled data outside approved workflows, including the full context of who, what, and where.
3. Fake recruiters and job offers: Foreign agents set up consultancies, think tanks, or HR firms. They rank applicants by access, request a “trial report,” and then move to encrypted apps. Fake interviews and take-home projects can give threat actors easy access to sensitive systems.
InnerActiv detects moonlighting and foreign recruiting patterns; on-screen OCR reads pitches in any language on personal webmail, LinkedIn, and messaging apps.
4. Planting agents inside companies: Remote hiring enables state-backed operators to apply at companies under false identities. After they’re hired, they have legitimate credentials to operate inside networks.
InnerActiv identifies the signals remote IT workers leave behind, such as multiple personal logins, hidden file transfers, remote control sharing, and suspicious notes.
5. Exfiltration through personal channels: Data rarely leaves via monitored corporate email. It moves through personal webmail, personal AI accounts, screenshots, printouts, and remote sessions.
InnerActiv detects exfil through personal webmail, shadow AI, and prompt histories, as well as printing, scanning, and copying activities.
InnerActiv complements existing security tools. It fills the missing context gap, giving security teams the evidence they need to ask the right questions early. To learn more about what human and AI agents are doing with your sensitive data, contact InnerActiv today.
About InnerActiv
InnerActiv sees what others can’t. Founded in 2009 and based in Columbus, Ohio, InnerActiv provides endpoint-native visibility and control over insider risk, fraud, data exposure, and AI usage. By combining process and file telemetry with display-level visibility, InnerActiv shows what every user and non-human identity actually does, helping organizations stop risky activity before it spreads.
Enable AI. Control the Risk.

The $6.3 Billion Heist That Started on One Laptop
Modern breaches rarely start by smashing through the perimeter. Increasingly, they start with access an organization has already granted. On October 29, attackers drained roughly $6.3 billion from Binance, the world’s largest crypto exchange. It is the biggest crypto theft on record, and most of the money was gone in about 20 minutes.